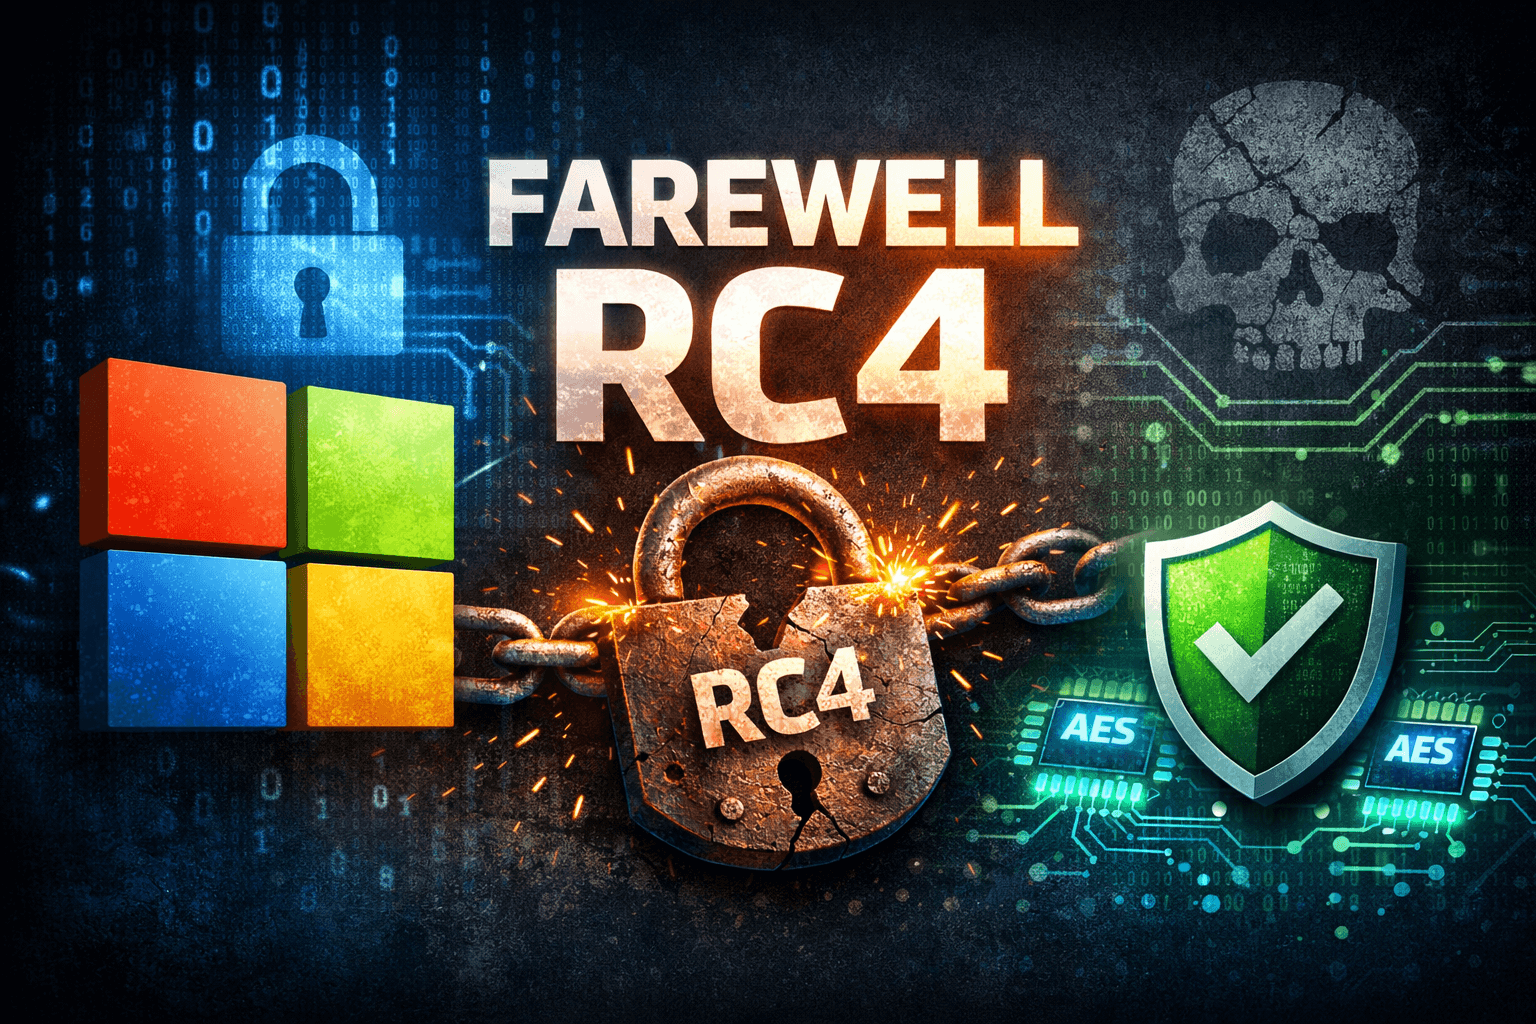
Microsoft has announced plans to disable a long-outdated encryption cipher that has been a persistent weak point in Windows security for more than 20 years. The change marks a significant shift away from legacy cryptography that modern attackers have repeatedly exploited.
The cipher in question is RC4, an encryption algorithm introduced in the 1990s that became deeply embedded in Windows authentication systems when Active Directory launched in 2000. Despite years of warnings from cryptographers and security professionals, RC4 has remained enabled by default in many Windows environments—until now.
Why RC4 Is a Problem
RC4 was designed in a different era, long before today’s computing power and attack techniques existed. Over time, researchers discovered structural weaknesses that make RC4 vulnerable to practical attacks. These flaws allow attackers to recover encrypted data far more easily than modern security standards would allow.
One of the most well-known attack techniques tied to RC4 is Kerberoasting. In this scenario, attackers extract encrypted Kerberos service tickets from a Windows domain and crack them offline. When RC4 is used, this process becomes significantly easier, often leading to privilege escalation and full domain compromise.
Despite these known risks, RC4 persisted largely because of backward compatibility concerns. Many organizations still rely on older systems, applications, or configurations that were never updated to use stronger encryption.
What Microsoft Is Changing
Microsoft plans to disable RC4 by default in Windows authentication systems starting in 2026. While the cipher won’t be immediately removed from the operating system, it will no longer be automatically used unless administrators explicitly re-enable it.
Instead, Windows will rely on stronger encryption algorithms—primarily AES-based ciphers—that are far more resistant to modern cryptographic attacks. This aligns Windows security defaults with long-standing best practices in the cybersecurity community.
Microsoft is also introducing better visibility into encryption usage. Administrators will be able to identify which systems, services, or applications are still attempting to use RC4, making it easier to remediate problems before enforcement fully takes effect.
What This Means for Organizations
For many modern environments, this change will be seamless. Organizations that already follow current security guidance and use updated systems are unlikely to notice any disruption.
However, environments that still depend on legacy applications, outdated devices, or misconfigured authentication settings may encounter issues once RC4 is disabled by default. Systems that haven’t been updated in years may fail authentication unless they’re reconfigured to support stronger encryption.
IT teams should treat this announcement as an early warning. Auditing Kerberos encryption settings, reviewing domain controller logs, and testing legacy systems now can prevent unexpected outages later.
A Long-Overdue Security Improvement
The retirement of RC4 represents a broader shift away from insecure defaults that have lingered in enterprise software for decades. While backward compatibility once justified keeping weak cryptography alive, today’s threat landscape makes that trade-off increasingly dangerous.
By finally moving away from RC4, Microsoft is closing a well-known attack vector and pushing Windows environments toward stronger, more resilient security practices—something security professionals have been calling for for years.
AUTHOR
Lovel is a contributor at OC Partnership, focusing on business trends, marketing, technology developments, and industry insights that help professionals stay informed and make better decisions. With a practical, research-driven approach, Lovel delivers clear and accessible content designed for business owners, marketers, and professionals.